
The most important capabilities Microsoft announces for its Sovereign Cloud today reach the Swiss regions without any action on your side. The larger part of the announcement is aimed at governments, critical infrastructure and regulated large enterprises. Douglas Phillips, President and CTO of Microsoft Specialized Clouds, described on 20 October 2026 how controls will be chosen per workload from now on: in the public cloud, on your own hardware or with a partner. We checked every announcement for availability in Switzerland and say what we recommend for typical situations.
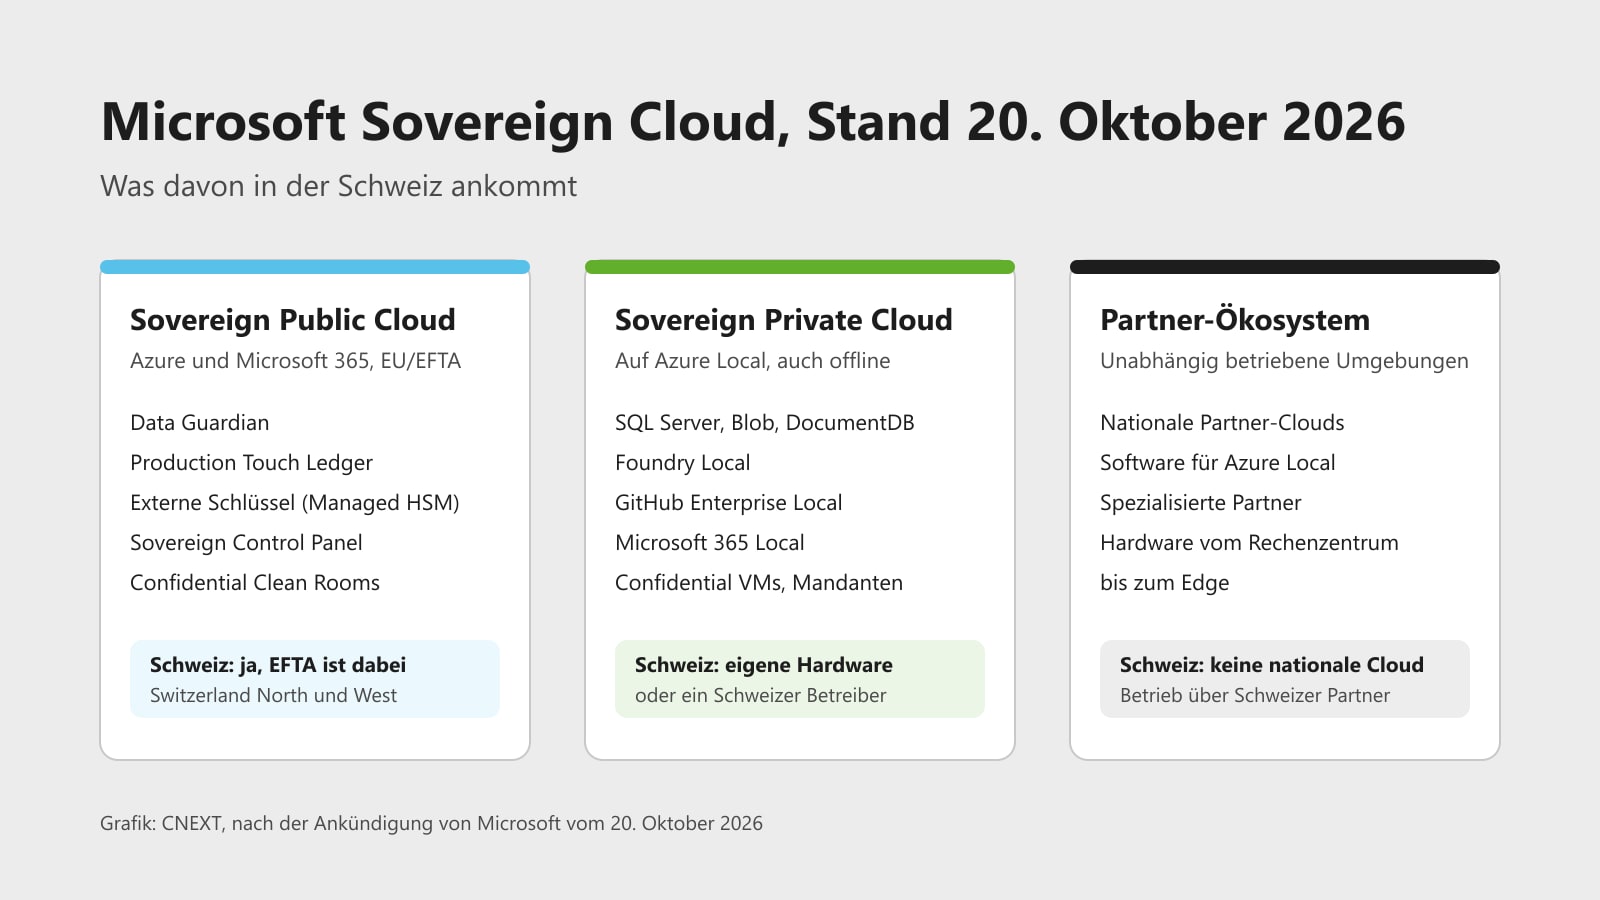
Graphic: CNEXT, after Microsoft's announcement of 20 October 2026.
What Microsoft announced
Microsoft arranges its sovereignty offerings in three tiers that an organisation combines per application. The Sovereign Public Cloud adds controls for data residency, confidentiality, access by Microsoft personnel and continuity in a crisis to the existing Azure and Microsoft 365 regions. The Sovereign Private Cloud brings the same services on Azure Local into a datacenter that the customer or an operator controls, with or without a connection to Microsoft. The partner ecosystem covers independently operated environments such as Bleu in France, software for Azure Local and specialised partners in each country.
For Swiss customers the most important line of the announcement is the geography. Data Guardian and the new Production Touch Ledger are rolling out for the EU and the EFTA, and Switzerland is an EFTA member. The access controls therefore apply to the Switzerland North region in Zurich and Switzerland West in Geneva as well, without any migration on your side.
Availability in Switzerland
As of 20 October 2026, checked against the announcement, Microsoft's documentation and the statements of Microsoft Switzerland. "Yes" means the capability can be used in the Swiss regions or on hardware in Switzerland as soon as Microsoft reaches the stated status.
| Capability | Status according to Microsoft | In Switzerland |
|---|---|---|
| Data Guardian: staff resident in Europe approve and monitor remote access by Microsoft engineers to production systems | Rolling out for the EU and the EFTA, phased, no date per region | Yes, the Swiss regions are EU/EFTA regions |
| Production Touch Ledger: tamper-evident record of that access and the actions taken | Phased rollout in the EU and the EFTA | Yes, with the same caveat on timing |
| Just-in-time access and Customer Lockbox: you approve each access by Microsoft to your data individually | Available; Customer Lockbox requires Microsoft 365 E5, Office 365 E5 or the compliance add-on | Yes, in Microsoft 365 and Azure |
| External key management with Azure Managed HSM: the root key stays in your own HSM or with a trusted third party | Generally available since 16 October 2026, enabled through the Microsoft account team, Private Link still in preview | Yes, Managed HSM runs in Switzerland North |
| Sovereign Control Panel: one view in the Azure portal for sovereignty posture, gaps, risks and continuity readiness | Public preview from Microsoft Ignite, 17 to 20 November 2026 | Expected yes, Microsoft names no region list |
| Azure Confidential Clean Rooms: several parties analyse shared sensitive data without disclosing it | Limited preview | On request, no region list published |
| Transition from connected to disconnected operations on Azure Local | Public preview | Yes, on your own hardware |
| SQL Server on Azure Local, connected and disconnected | Generally available | Yes, on your own hardware |
| DocumentDB and Blob Storage on Azure Local | Public preview | Yes, on your own hardware |
| Foundry Local on Azure Local: models, knowledge, tools and agents run locally, with an expanded model catalogue | Generally available from Ignite | Yes, the models process on your hardware |
| GitHub Enterprise Local: GitHub Enterprise Server as a validated appliance, GitHub Copilot with locally hosted models | Generally available from Ignite | Yes, on your own hardware |
| Microsoft 365 Local: SharePoint Server and Exchange Server on Azure Local; new integration with Foundry Local for search and answers over local data | Available; the Foundry integration in preview for approved customers | Yes; ELCA announced operation in Switzerland in June 2026, starting with local extensions for existing Microsoft 365 customers |
| Confidential virtual machines on Azure Local | Generally available | Yes |
| Multitenancy on Azure Local | Announced, no date | Not yet |
| National Partner Cloud, operated independently of Microsoft | Bleu in France | No, none announced for Switzerland |
Outside today's announcement but relevant to the same decision: Microsoft 365 processes customer data within the EU Data Boundary, which includes the EFTA and therefore Switzerland. In-country processing of Copilot interactions in Switzerland was announced by Microsoft in November 2025 for 2026; we have not found a confirmation to date that it is live.
What we recommend
Microsoft now decides per workload which tier applies. Our recommendation follows the same logic: a list of your applications with their data class, and the matching tier per row.
You work on Microsoft 365 and no regulator prescribes your operations. Nothing changes in your operations, and there is nothing to buy. Data Guardian and the ledger reach your regions through the rollout. Customer Lockbox requires Microsoft 365 E5 or the compliance add-on; if you have it licensed, check that it is switched on. Record today's status in your data protection documentation. You need Azure Local only once an application has to run without internet or on your own hardware.
You are subject to FINMA, professional secrecy or cantonal rules. The Sovereign Public Cloud covers most requirements once you set up the following: external key management for the services holding sensitive personal data, a Sovereign Landing Zone that enforces regions and encryption by policy, and from Ignite the Sovereign Control Panel as evidence for auditors. The Data Guardian logs belong in your audit file. How we build an Azure environment under these rules is described on our Azure page.
You run critical infrastructure or need operations without internet. Then Azure Local is the right place, for the one application that really demands it. SQL Server runs there today, Foundry Local and GitHub Enterprise Local follow in November. For SharePoint and Exchange on site, Microsoft 365 Local is ready, on your own hardware or with a Swiss operator such as ELCA, which announced its offering in June 2026. Add up hardware, licences and the operations team before you decide; the difference to the public cloud lies in the operations you take on yourself.
Limits
What Microsoft promises for Ignite is an announcement. Preview features change, and Data Guardian and the ledger have no date per region yet. We will update the table after Ignite.
Data Guardian governs access by Microsoft personnel. It does not change where AI models compute. In Microsoft Foundry, newer models process in the EU data zone, which does not include Switzerland, or globally; which models run in Switzerland North is listed in our guide to data boundaries.
The announcement names no prices. Azure Local needs validated hardware from manufacturers such as Dell, HPE or Lenovo, plus licences and a team that applies updates. We clarify these costs with you per application before a decision is made.
Next step
Which of your applications need which tier? Send us your list with the data class per application. You get the table back with our recommendation per row and the state of availability in Switzerland. I look forward to the conversation.
Marcel Haas, CEO CNEXT
Sources: Douglas Phillips, "Advancing digital sovereignty with greater control and choice", Microsoft, 20 October 2026. Microsoft Switzerland, "How Microsoft is addressing digital sovereignty in Switzerland", 25 February 2026. Microsoft Switzerland and ELCA, announcement at the Digital Sovereignty Day in Bern, 16 June 2026. Microsoft Learn, Data Guardian overview and EU Data Boundary. Azure update AZ574296, External key management for Azure Key Vault Managed HSM generally available, 16 October 2026. Microsoft, announcement of in-country processing of Copilot interactions, November 2025. All facts checked on 20 October 2026. Related: Microsoft 365 and data residency in Switzerland.